Educational Portal Web Application VAPT Case Study
An authorized security assessment of an educational web portal, focused on authentication, access controls, input validation and OWASP Top 10:2025 risks.
The engagement combined manual and tool-assisted testing to evaluate the portal’s security controls and identify potential weaknesses within the approved scope. Authentication, authorization, session management, user-controlled inputs, business logic and security configurations were carefully reviewed. All potential findings were manually validated, risk-rated and documented with practical remediation guidance. Client identity, sensitive evidence and technical details have been removed from this public case study.
- OWASP Top 10:2025
- Authentication Testing
- Access Control Testing
- Session Management
- Input Validation Testing
- Business Logic Review
- Security Configuration
- Risk-Based Reporting
Category
Web Application & API VAPT
Clients
Confidential Educational Organization
Location
Confidential / Remote
Published
August 31, 2026
Project Summery
This project involved an authorized Web Application Vulnerability Assessment and Penetration Testing engagement for an educational portal. The objective was to evaluate the application’s security controls, identify potential weaknesses and provide practical guidance for reducing security risks.
The assessment combined manual and tool-assisted testing across authentication, access control, session management, input validation, business logic and security configurations. Testing followed the approved scope and was aligned with the OWASP Web Security Testing Guide and relevant OWASP Top 10:2025 risks. Potential findings were manually validated, prioritized by risk and documented with remediation recommendations. Client identity, sensitive evidence and technical details remain confidential.
Security Challenge
Educational web portals may process student records, employee information, account credentials and administrative data. Weak authentication, broken access controls, insecure sessions or unsafe input handling could expose sensitive information and disrupt important academic services.
The objective was to assess whether the authorized application scope provided appropriate protection against realistic web security risks without affecting normal portal operations.
Assessment Objectives
The Web Application VAPT engagement focused on the following objectives:
- Identify security weaknesses within the approved scope.
- Evaluate authentication and account-security controls.
- Review authorization restrictions between approved user roles.
- Assess session and cookie security.
- Test user-controlled inputs for common web vulnerabilities.
- Review application security headers and configurations.
- Examine selected business workflows for potential misuse.
- Validate potential findings to reduce false positives.
- Provide practical and prioritized remediation guidance.
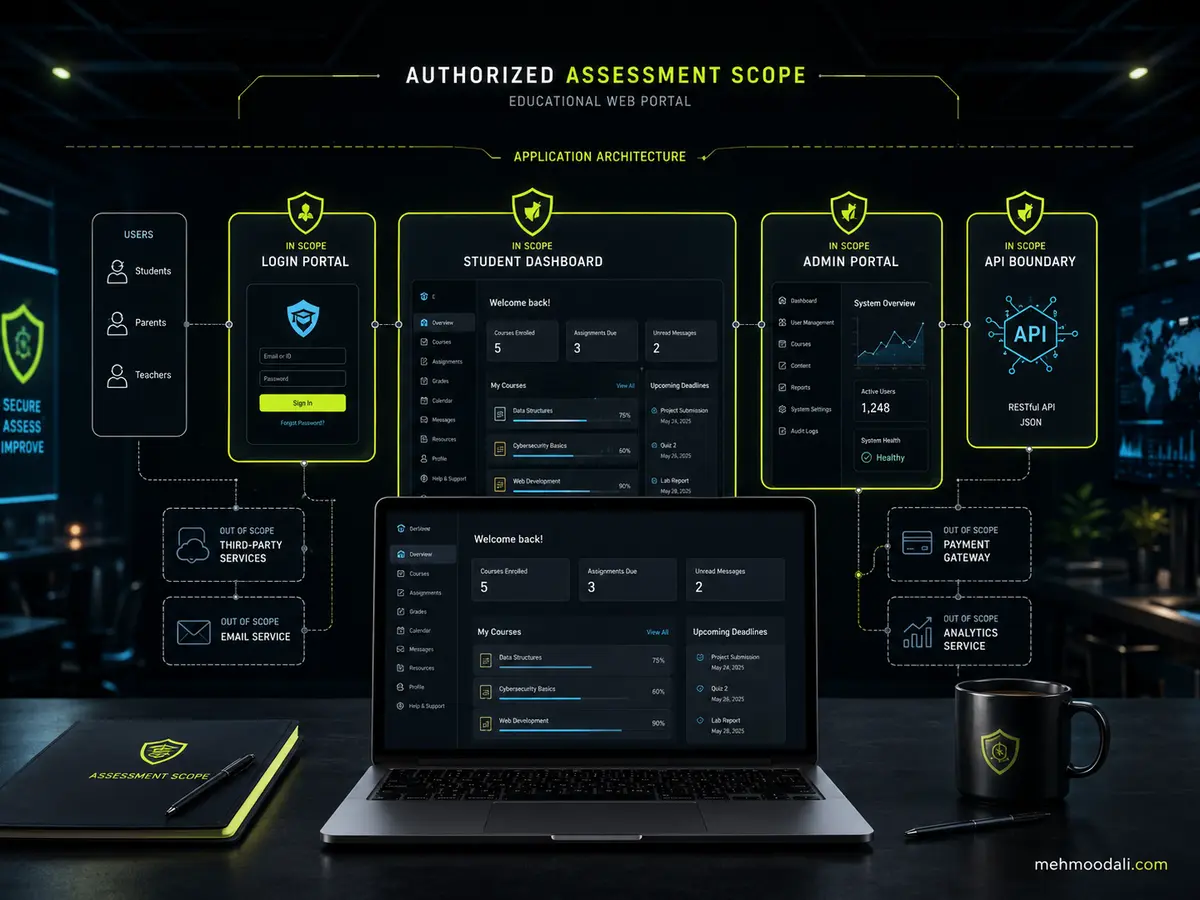
Authorized Assessment Scope
The assessment was limited to application components and user roles explicitly approved by the organization.
The authorized scope included:
- Publicly accessible portal pages
- Authentication and login functionality
- Approved authenticated user roles
- Student-facing application features
- Selected administrative functions
- Session-management controls
- User-controlled input fields
- Application error handling
- Security headers and configurations
- Approved API endpoints
All testing was performed within defined rules of engagement and agreed testing boundaries.
Scope Limitations and Exclusions
The following activities were excluded unless separately authorized:
- Denial-of-service or availability testing
- Destructive exploitation
- Social-engineering attacks
- Physical-security testing
- Testing third-party services
- Accessing systems outside the approved scope
- Downloading unnecessary sensitive information
- Modifying or deleting production data
- Publishing client-identifying information
These restrictions helped protect business operations, user privacy and third-party systems throughout the assessment.
Web Application VAPT Methodology
The assessment followed a structured methodology aligned with the OWASP Web Security Testing Guide and relevant OWASP Top 10:2025 risk categories.
1. Scope Validation
The approved application components, testing environment, user roles, limitations and communication procedures were confirmed before security testing began.
2. Information Gathering
The authorized application attack surface, visible technologies, accessible functions and publicly exposed security controls were reviewed.
3. Authentication Testing
Login workflows, account behavior, password-related features and authentication protections were evaluated for potential weaknesses.
4. Session Management Testing
Session cookies, expiration, logout behavior and other session controls were assessed to determine whether authenticated sessions were handled securely.
5. Authorization Testing
Approved user roles and application functions were reviewed to determine whether access restrictions were consistently enforced.
6. Input Validation Testing
User-controlled inputs were assessed for unsafe handling, injection risks and unexpected application behavior.
7. Business Logic Review
Selected portal workflows were manually evaluated for misuse scenarios that automated vulnerability scanners may not identify.
8. Security Configuration Review
Security headers, application responses, error messages and exposed configuration information were reviewed for potential weaknesses.
9. Manual Validation
Potential findings were manually examined to reduce false positives and confirm their technical relevance within the approved scope.
10. Risk Analysis and Reporting
Validated findings were assessed according to severity, exploitability and potential business impact. Practical remediation recommendations were then prepared for technical and management stakeholders.
Security Areas Tested
The engagement evaluated security controls related to:
- Authentication security
- Authorization and access control
- Session management
- Input validation
- Injection risks
- Security misconfiguration
- Sensitive data handling
- Cryptographic protection
- Error handling
- Business logic
- Application components
- Logging and monitoring
- Approved API security
- Client-side security
Testing a security area does not automatically mean that a vulnerability was discovered in that area.
Tools and Technologies
The assessment combined manual security analysis with approved testing tools.
Tools used may include:
- Burp Suite Professional
- Nmap
- OWASP ZAP
- Browser developer tools
- Controlled testing scripts
- CVSS-based risk assessment
Only tools genuinely used during this engagement should remain in the published version.
Findings and Risk Analysis
Detailed vulnerability information, exploitation evidence and affected components remain confidential. Any confirmed findings were documented in the private assessment report with:
- Finding title and severity
- Affected component
- Technical description
- Sanitized supporting evidence
- Potential business impact
- Reproduction information
- Recommended remediation
- Retesting guidance
- Relevant OWASP references
The public case study intentionally excludes information that could expose the client, application or users to additional security risks.
Public Findings Overview
Add the following information only after confirming it from the real assessment report:
- Critical findings: 3
- High-risk findings: 8
- Medium-risk findings: 2
- Low-risk findings: 105
- Informational observations: 126
If client approval is unavailable, remove this complete numerical section rather than estimating the results.
Assessment Deliverables
The engagement produced security documentation designed for technical and management stakeholders.
Deliverables included:
- Executive summary
- Authorized scope and limitations
- Testing methodology
- Risk-rated findings
- Sanitized technical evidence
- Business-impact explanations
- Practical remediation guidance
- Prioritized remediation plan
- Retesting recommendations
Project Outcome
The assessment provided the organization with a structured view of its web application attack surface and the security controls requiring attention.
Combining manual testing with approved security tools helped examine authentication, authorization, session management, input handling, business logic and application configurations more thoroughly than automated scanning alone.
The resulting report provided practical information that developers and system administrators could use to prioritize remediation and strengthen the portal’s security posture.
No claim is made that the application became completely secure. Security requires continuous monitoring, secure development, periodic testing and verification after changes.
Authorization and Confidentiality
This Web Application VAPT engagement was conducted only within an authorized scope and agreed rules of engagement.
Client names, domains, IP addresses, credentials, personal data, vulnerability evidence and detailed exploitation information have not been included in this public case study.
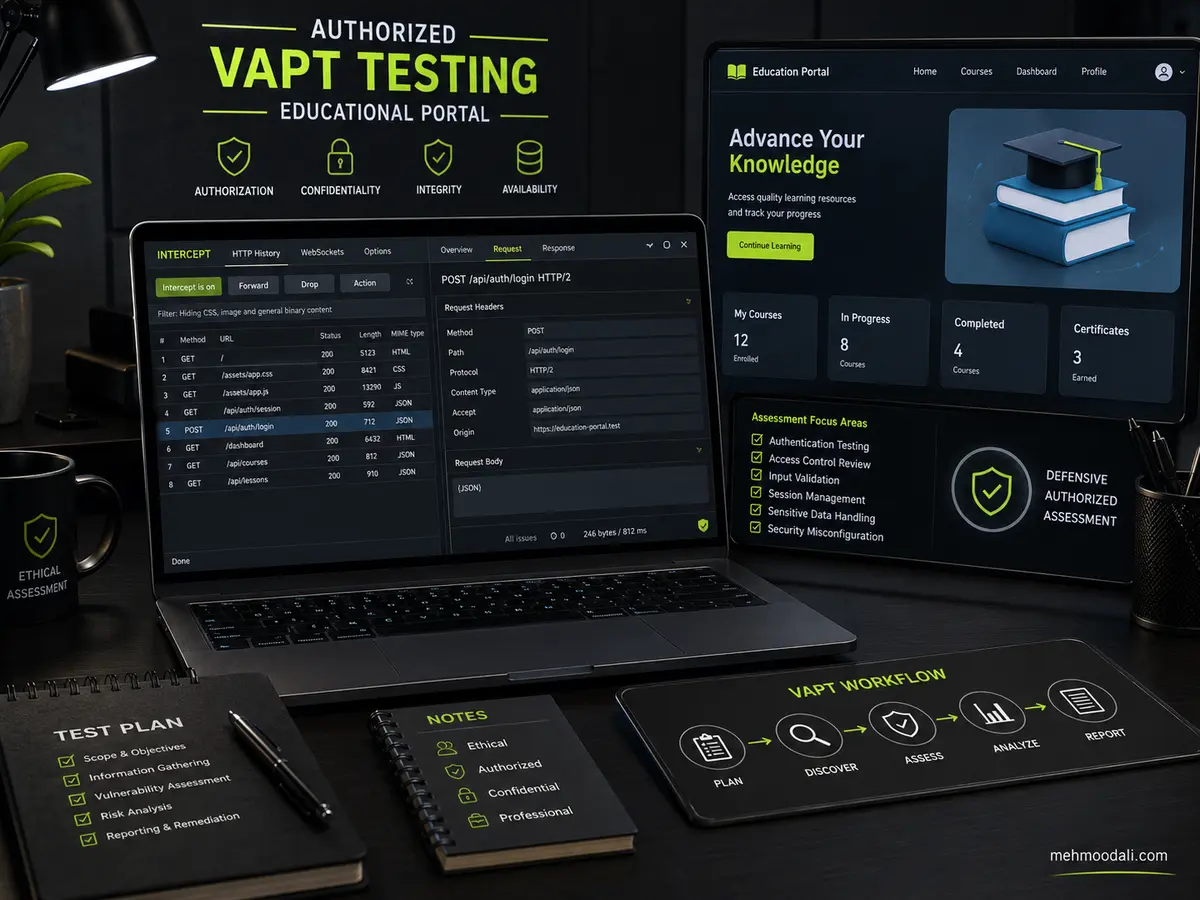
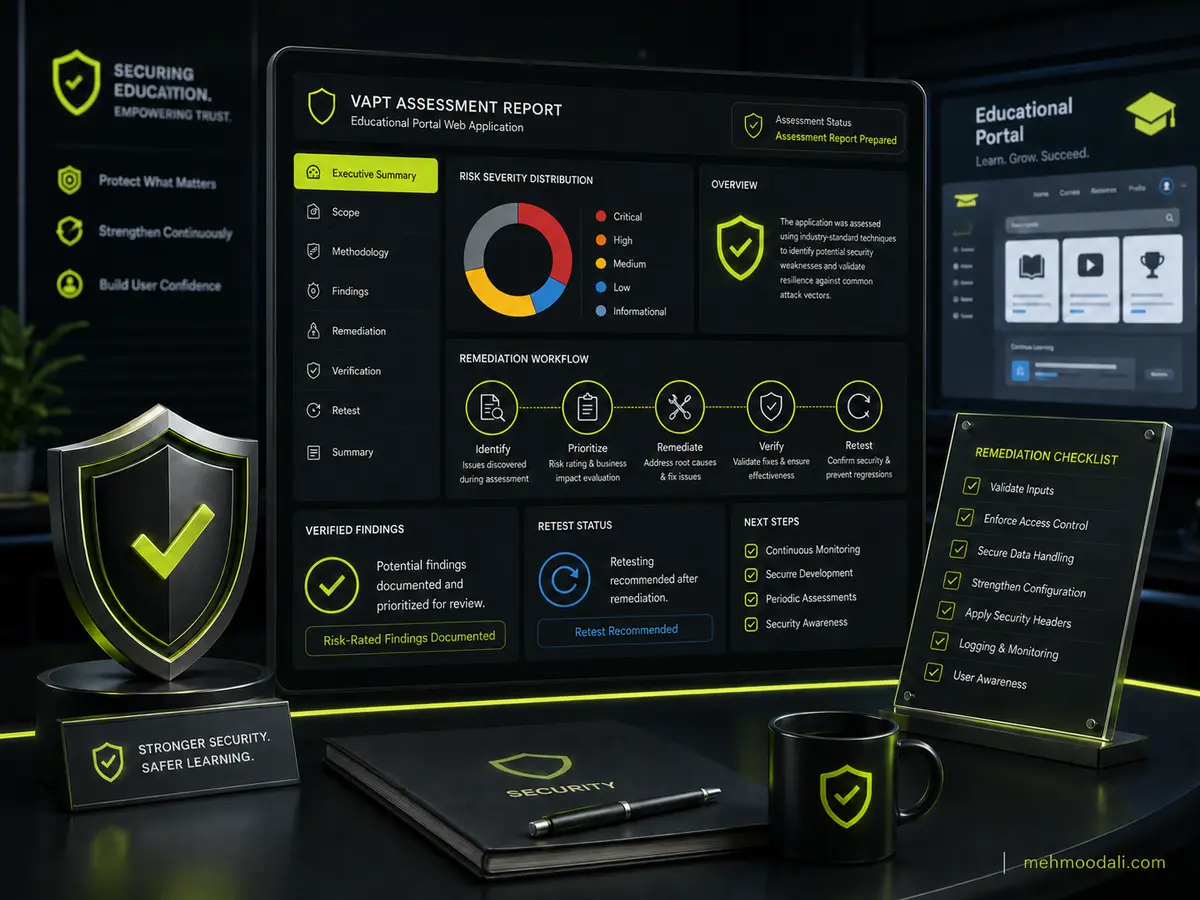
The accompanying images are illustrative visualizations created for this public portfolio. They are not screenshots of the client’s application, security tools or assessment results.
About the Security Consultant
This assessment was prepared by Mehmood Ali, a cybersecurity consultant and penetration tester with hands-on experience across vulnerability assessment, web application security, security operations, digital forensics and Microsoft security.
His professional background combines offensive security testing with defensive security, incident analysis and technical training. This allows findings to be communicated from both an attacker-risk and practical-remediation perspective.
View the complete professional profile, certifications and security experience on the About Me page.
Relevant Certifications
Relevant professional credentials include:
Certified Ethical Hacker | CEH
Certified SOC Analyst | C|SA
Penetration Testing
Vulnerability Management
Computer Hacking Forensic Investigator | CHFI
Certified EC-Council Instructor | CEI
Microsoft Security Operations Analyst Associate | SC-200
Microsoft Cybersecurity Architect Expert | SC-100
Frequently Asked Questions
What is a Web Application VAPT assessment?
Web Application VAPT combines vulnerability assessment and controlled penetration testing to identify, validate and prioritize security weaknesses in web applications.
Which methodology was followed?
The assessment approach was aligned with the OWASP Web Security Testing Guide and relevant OWASP Top 10:2025 security risks.
Does VAPT rely only on automated vulnerability scanners?
No. A professional assessment combines automated discovery with manual testing, access-control review, business-logic analysis and finding validation.
Was the educational portal tested with authorization?
Yes. Testing was limited to the approved application scope, user roles and rules of engagement defined for the assessment.
Why are the client and vulnerability details hidden?
Detailed findings could expose the organization, its users or its technical environment to unnecessary risk. Client identity and sensitive evidence remain confidential.
Can remediation and retesting be included?
Yes. Remediation guidance can be provided for validated findings, followed by authorized retesting after corrective actions are implemented.
References and Testing Standards
- OWASP Top 10:2025
- OWASP Web Security Testing Guide
- OWASP API Security Top 10
- Common Vulnerability Scoring System
- Applicable vendor security guidance
Need a Web Application Security Assessment?
Protect your customer portal, educational platform, business application or administrative dashboard with an authorized and confidential Web Application VAPT assessment.
Contact Mehmood Ali to discuss your application scope, testing requirements, reporting expectations and remediation support.